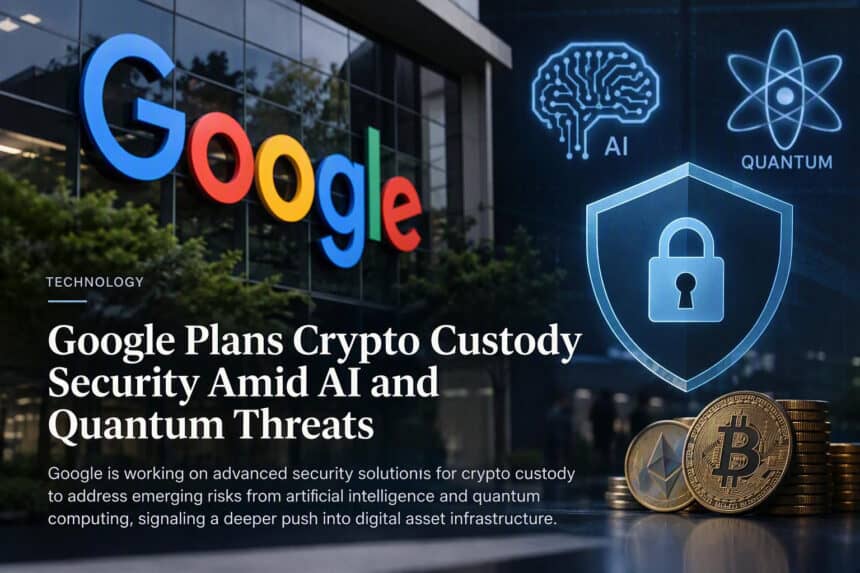
Google plans to launch a new crypto custody security system to help banks and other financial firms protect digital currencies from cyberattacks, compromised private keys and emerging tech threats. Google Multi-Party Compute (MPC) uses a cryptographic method that divides private keys into separate shares instead of storing the entire key in a single place.
The move follows advances in artificial intelligence (AI) and concerns about the security of blockchain networks and digital asset infrastructure due to future capabilities of quantum computing.
Google Multi-Party Compute: A New Hope for Institutional Crypto Security
Google Multi-Party Compute is currently in private preview with large financial institutions and is expected to be commercially available in early 2027. The company unveiled the initiative on Oct. 28, in conjunction with the Digital Asset Security and Multi-Party Computation Symposium in New York City.
The technology is meant to help banks and other organizations securely store, manage and transfer cryptocurrencies and other digital currencies. Alphabet, the parent company of Google, is also employing the system to safeguard its own assets on the Ethereum and Solana blockchains.
The platform uses multi-party computation to break a private key into multiple shares, which are then spread across different environments. For example, a financial institution might store one share on its own hardware, another on Google Cloud, and a third with another provider. The net result is that you don’t need to have any one machine holding the entire private key.
Google says customers still control their keys and the company cannot access the shares in unencrypted form, even if those shares are stored on its infrastructure. The system is intended to reduce the risk of unauthorized access by reducing the dependence on a single storage location and to prevent a compromised machine from exposing an entire key.
Risks to crypto security are growing due to AI and quantum computing
Artificial intelligence is opening up new possibilities for cybersecurity teams, but it is also providing attackers with tools to pinpoint vulnerabilities in software, examine blockchain systems and uncover flaws in digital asset infrastructure. These developments are putting pressure on financial institutions to strengthen security controls around private keys and transaction authorization.
Already, researchers have discovered vulnerabilities in blockchain software that could be exploited with serious consequences. A case in point is a reported vulnerability in the XRP Ledger that could have allowed the creation of unauthorized XRP tokens. This case highlights the need for timely security reviews and software fixes.
Vitalik Buterin, the co-founder of Ethereum, has also warned about the impact of AI-driven advances in mathematics on cryptographic security. Worries include the possibility that AI could speed up the discovery of weaknesses in cryptographic methods, which could affect systems that rely on lattice-based cryptography.
The quantum computer is another long-term challenge. There is no quantum computer today that can crack the widely used cryptography in the blockchain, but analysts estimate that perhaps 6.9 million Bitcoin could be at risk of a future quantum attack because their public keys have been exposed.
The primary goal of Google’s MPC system is to safeguard private keys and to stop unauthorized transactions. However, it should not be confused with a complete fix to quantum vulnerabilities in blockchain protocols.
The Growing Importance of Institutional Crypto Custody
The plans for the launch underline the growing link between traditional finance and crypto. Banks, asset managers and other financial firms need secure infrastructure to custody cryptocurrencies, manage tokenized assets and support blockchain-based financial services.
Institutional custody is moving beyond the mere storage of digital possessions. Today’s solutions need to cover transaction authorization, control of access, operational resilience and compliance requirements, while reducing the risks stemming from compromised credentials.
Google’s proposed MPC platform could help institutions spread the responsibility for security across multiple environments without losing control of their private keys. Its commercial release in early 2027 may give financial institutions another option for protecting digital property.
But institutions will need to assess the platform’s implementation, recovery processes, compatibility and overall security prior to rolling it out at scale.
Conclusion
AI-enhanced cyber attacks and risks posed by quantum computing are getting increased attention. Google’s Multi-Party Compute system is a major step in institutional crypto custody. The platform distributes private key shares across different environments to reduce single points of failure and enhance transaction security.
The system could help banks and financial institutions that want to move into digital investments and is aiming for commercial availability in early 2027. However , MPC targets certain custody risks , not all blockchain security risks . So , general cybersecurity and long-term cryptographic upgrades are critical .